
Wiki / Exposed files
Risk: Publicly accessible
Anyone who adds /.env to your address can download the application's settings file with its passwords. It usually holds the database password, the mail login, and keys for payments and other services. Close it today and change everything that was in it.
What it does not mean. It is not proof that someone has already downloaded the file. The server access log shows that: look for requests to /.env answered with 200.
- In our report
- Risk (red), the highest category weight, 2.0
- Time to fix
- 5 minutes to close; changing the secrets takes an hour or more
- Can it break things
- Closing: no. Changing secrets: yes, if the new values are not written to
.env
How to fix it
Our check counts the file as exposed only when the response contains lines of the form NAME=value, so this is the real file, not an error page.
nginx (tested on 1.26.3)
location ~ /\.(?!well-known/) {
    return 404;
}On the test server the response for /.env and /sub/.env changed from 200 to 404. The same rule closed .env.production, .htaccess and .DS_Store, while /.well-known/acme-challenge/ stayed at 200: certificates are renewed through that path. Put it above other regular-expression location blocks: nginx uses the first one that matches.
Apache (tested on 2.4.59, also works in .htaccess)
RedirectMatch 404 "/\.(?!well-known/)"Needs mod_alias. Same result on the test server as with nginx.
More reliable: keep the file above the web root
mv .env ../.envOn the test server, once the file sat one level above the web root, the answer was 404 with no rule at all. The application has to be told the new location. Laravel projects need no move: the web root must be public/, which leaves .env outside it.
After closing: the secrets
grep -E "PASSWORD|SECRET|KEY|TOKEN" .envThe command lists what has to be changed. Change each value where it was issued (the database, the mail service, the payment provider's account) and only then write it to .env. Closing the file does not cancel the old passwords.
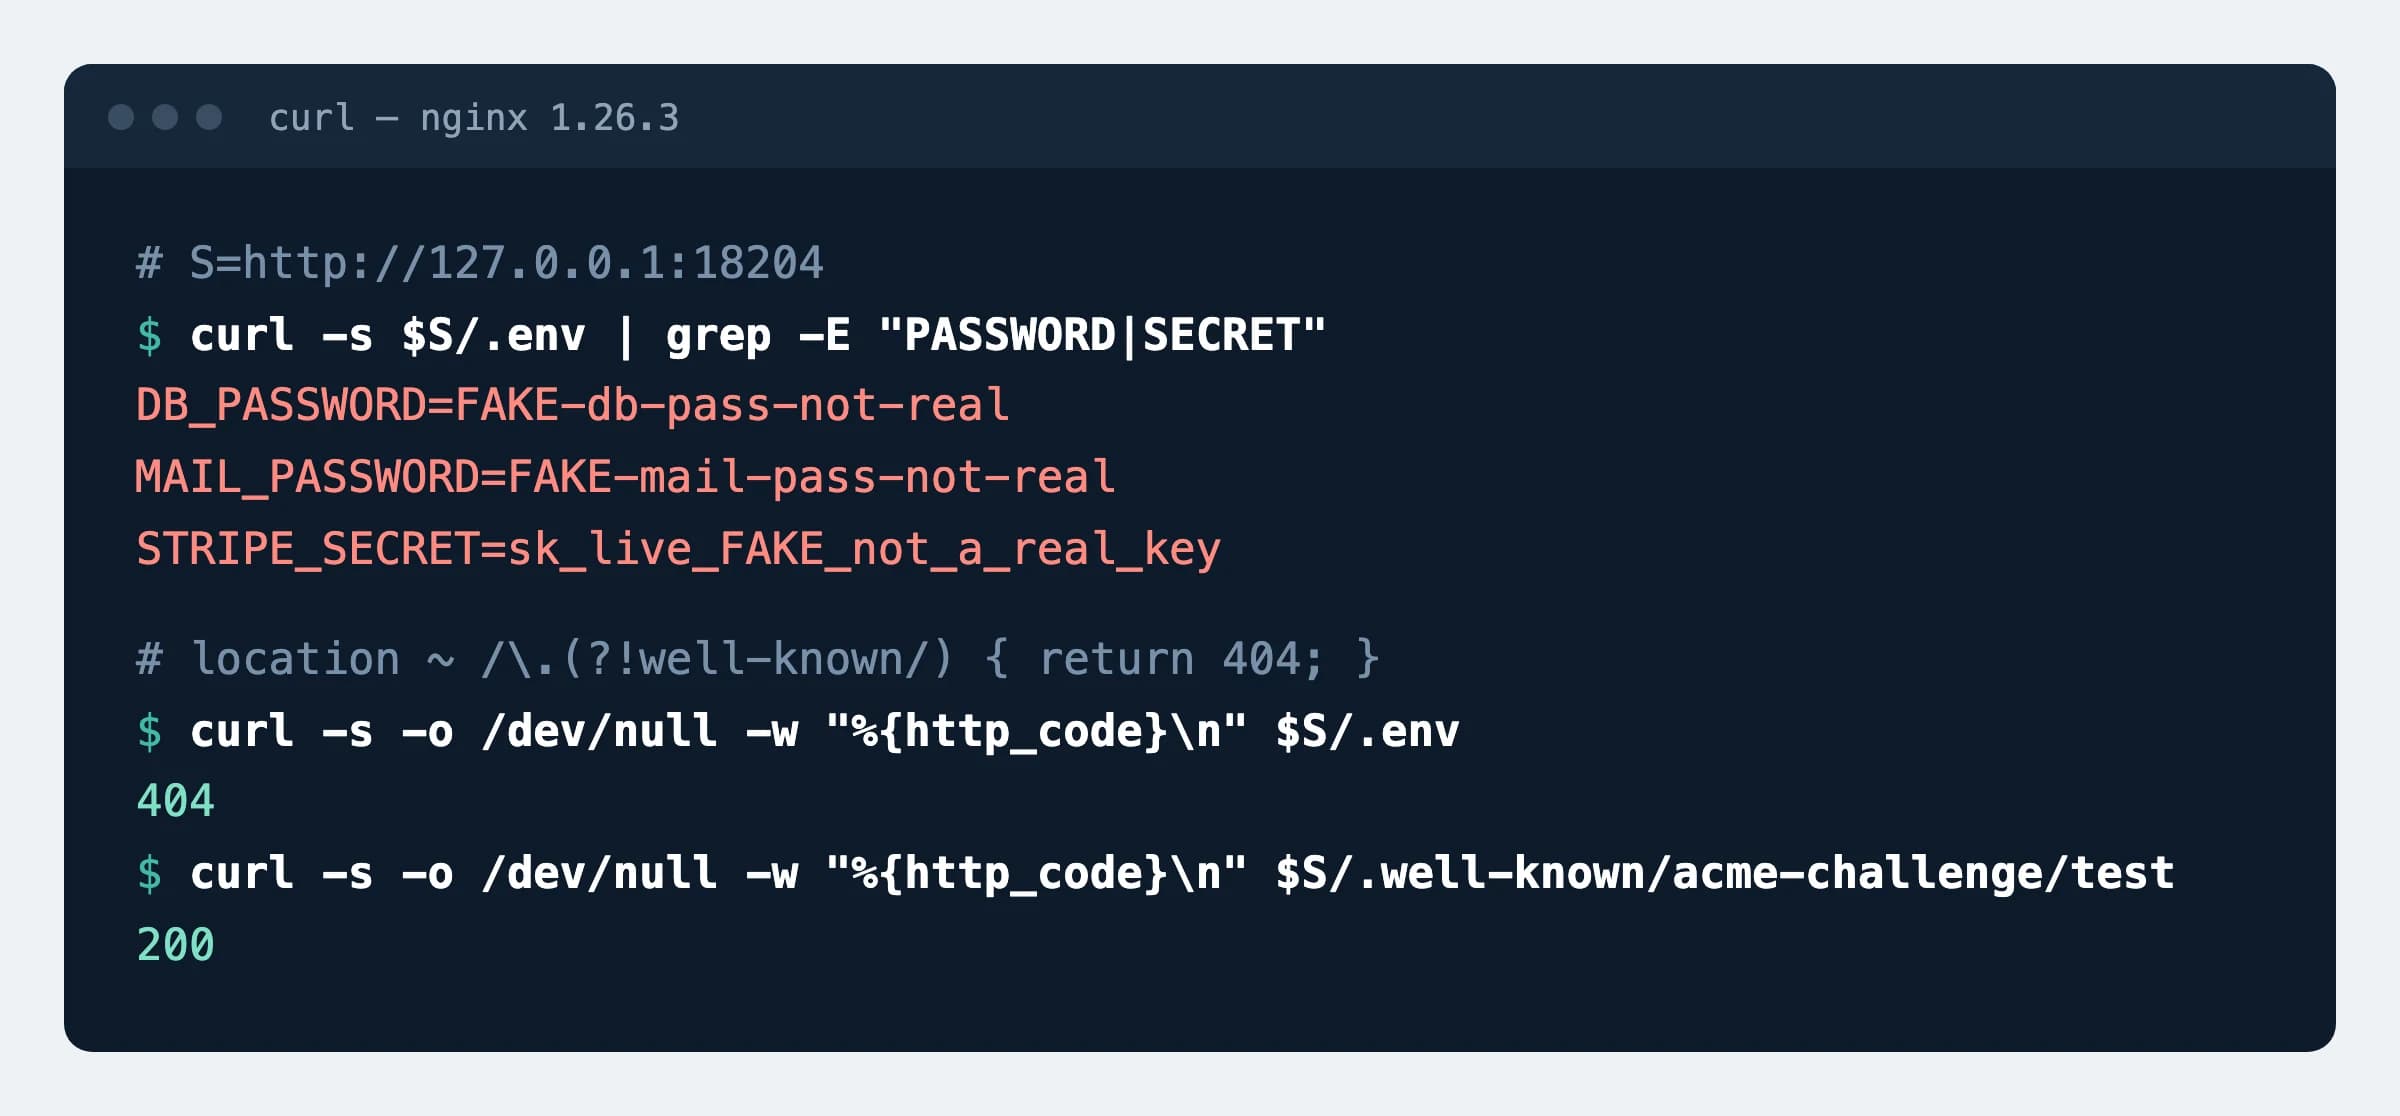
How to check
curl -s -o /dev/null -w "%{http_code}\n" https://example.com/.envExpected
404A 200 response means the file is still open. In a browser use a private window: it may show an old copy.
What can break
- If you change the database password without writing it to
.env, the site can no longer connect to the database. Change both places in one go. - Laravel with cached configuration (
php artisan config:cache) no longer reads.env: run the command again after the change. - The rule hides every file and folder whose name starts with a dot, except
/.well-known/. If you serve another such path to browsers on purpose, add an exception for it.
Our data
45
of 73,386 inspected .lt websites (0.06%) serve the contents of their .env file. Dataset, 16 November 2026
Sources
- nginx documentation: location (matching order)
- Apache documentation: RedirectMatch
- Laravel documentation: Deployment (public/ as web root, configuration caching)
- RFC 8555: ACME, section 8.3 (the /.well-known/acme-challenge/ path)
- AGuard: security dataset of Lithuanian websites, DOI 10.5281/zenodo.24282573
Changes
- Page published; nginx and Apache rules tested on a test server.