
Wiki / Exposed files
Risk: .git/ directory is publicly accessible
Anyone can download the full source code of the site with its change history from your server, including every password that was ever committed to the repository. Close it today: it takes one line.
What it does not mean. It is not proof that someone has already downloaded the code. The server access log shows that: look for requests to /.git/.
- In our report
- Risk (red), the highest category weight, 2.0
- Time to fix
- 5 minutes to close; changing the passwords takes longer
- Can it break things
- No.
git pullon the server keeps working
How to fix it
Turning off directory listing does not help: the names of .git files are known in advance and the rest are found from their contents. The path itself has to be blocked.
nginx (tested on 1.26.3)
location ~ /\.git {
    return 404;
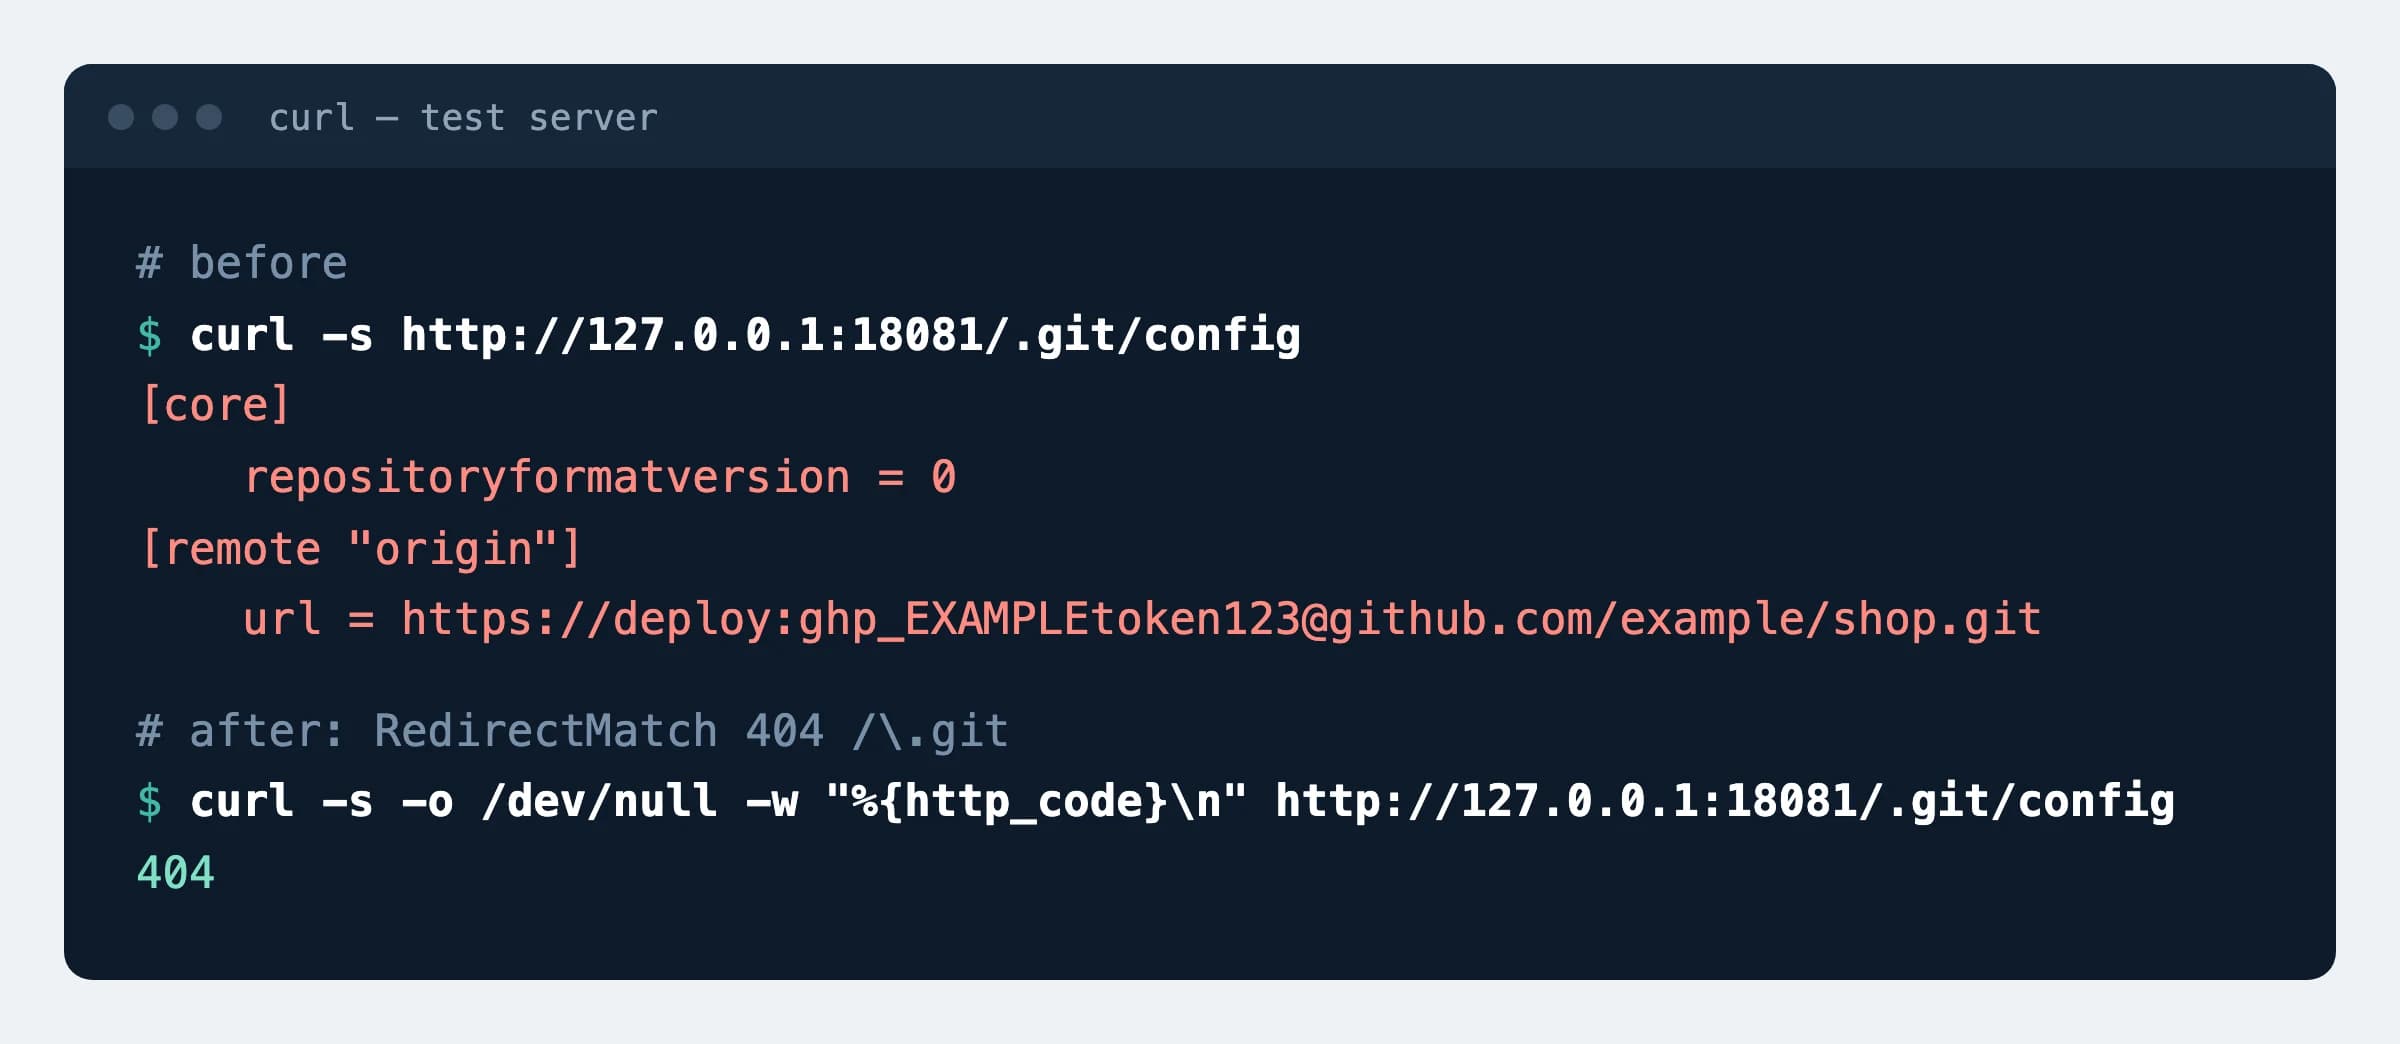
}On the test server the response for /.git/config and /.git/HEAD changed from 200 to 404, in a subdirectory too (/sub/.git/config). deny all also closes it but answers 403, which confirms the directory exists.
Apache (tested on 2.4.59, also works in .htaccess)
RedirectMatch 404 /\.gitNeeds mod_alias, which is enabled almost everywhere. Both rules also close .gitignore: the site does not need it.
After closing: passwords
git log --all --full-history -- .env wp-config.php config.phpThe command shows whether these files were ever in the repository. If so, change every password and key they held: a file deleted in a later commit stays in the history. Check .git/config too: it often holds the repository address with an access token.
For good: deploy without .git
rsync -a --exclude='.git' ./ server:/var/www/site/The most reliable setup is one where the site folder has no .git directory at all.
How to check
curl -s -o /dev/null -w "%{http_code}\n" https://example.com/.git/HEADExpected
404A 200 response with the text ref: refs/heads/main means the directory is open.
What can break
- Nothing changes for the site: the rule affects only requests made through a browser, while
git pullon the server works with the files directly. - Closing the directory does not undo a leak. Until the passwords are changed, the problem is not solved.
Our data
126
of 73,386 inspected .lt websites (0.17%) serve the contents of their .git directory. Another 45 expose an .env file. Dataset, 16 November 2026
Sources
- Git documentation: repository layout
- nginx documentation: location
- Apache documentation: RedirectMatch
- AGuard: security dataset of Lithuanian websites, DOI 10.5281/zenodo.24282573
Changes
- Page published; nginx and Apache rules tested on a test server.