
Wiki / Security headers
Risk: Strict-Transport-Security (HSTS)
The site works over HTTPS but does not tell browsers to always use it, so the first request of each visit can be intercepted on a shared network. It is not an emergency: one line and 10 minutes fix it.
What it does not mean. It does not mean the site has no HTTPS or a bad certificate. Those are checked in separate lines of the report.
- In our report
- Risk (red), category weight 1.0 of 2.0
- Time to fix
- 10 minutes if every subdomain already runs on HTTPS
- Can it break things
- Yes: subdomains without HTTPS stop opening
How to fix it
First make sure HTTP redirects to HTTPS: a browser must ignore this header when it arrives over an unencrypted connection. Start with max-age=300 (5 minutes), test the site and its subdomains, then raise it to a year.
nginx (tested on 1.26.3)
add_header Strict-Transport-Security "max-age=31536000; includeSubDomains" always;Goes into the server block that listens on 443. Without always the header is missing on error pages (404, 500). If a location has its own add_header, the server-level headers no longer apply there: repeat the line.
Apache (tested on 2.4.59, also works in .htaccess)
Header always set Strict-Transport-Security "max-age=31536000; includeSubDomains"Needs mod_headers. With Header set and no always, the header is missing on 404 and other error responses.
Cloudflare
SSL/TLS → Edge Certificates → HTTP Strict Transport Security (HSTS) → Enable HSTSSettings: Max Age Header (1 to 12 months), Apply HSTS policy to subdomains, Preload. If the origin server already sends the header, keep one source only.
How to check
curl -sI https://example.com | grep -i strict-transport-securityExpected
strict-transport-security: max-age=31536000; includeSubDomainsAn empty result means the header is missing. Repeat with an address that does not exist (for example /missing) to confirm the header is sent on error pages too.
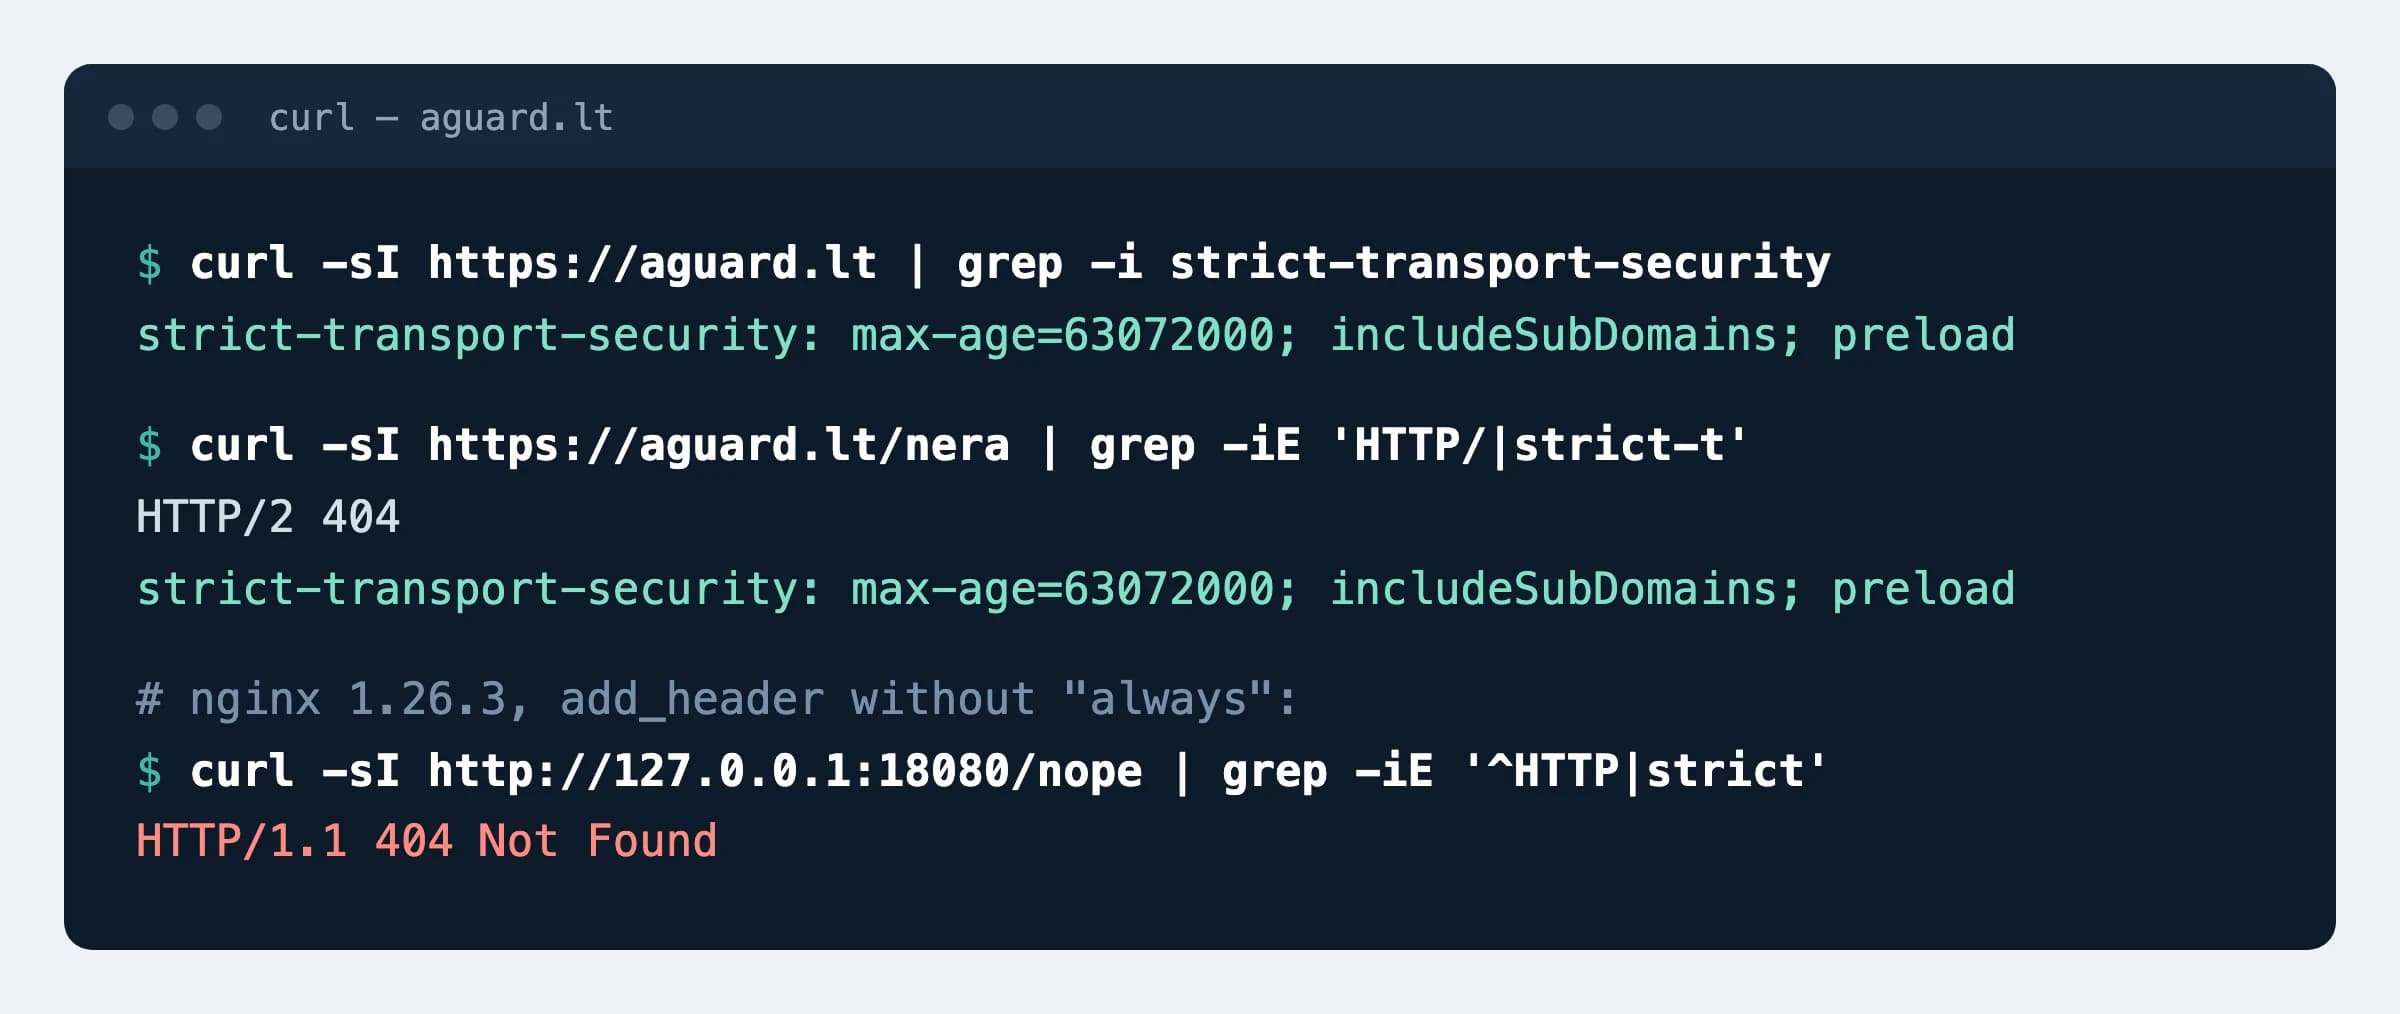
always: the 404 response has no header.What can break
- With
includeSubDomainsthe browser refuses any subdomain without HTTPS: an oldintranet.,mail.or a printer interface. Go through the DNS zone before you turn it on. - If HTTPS is switched off before
max-ageruns out, visitors who have already been to the site cannot open it until the period ends. The browser offers no way past the warning. - A header sent only over HTTP does nothing: the browser ignores it (RFC 6797, section 8.1).
Possible values
| Value | What it does | When to choose it |
|---|---|---|
max-age=300 | The browser remembers the rule for 5 minutes | Testing on day one |
max-age=31536000 | Remembers it for a year | The permanent value; the minimum the preload list accepts |
includeSubDomains | The rule covers every subdomain too | When every subdomain has a valid certificate |
preload | Allows the domain into the list built into browsers | Only if HTTPS stays forever: removal takes months to reach users |
max-age=0 | Tells the browser to forget the rule | When you need to switch HSTS off |
Our data
8.33%
of 73,386 inspected .lt websites (6,111) send HSTS without includeSubDomains, which leaves their subdomains unprotected. The dataset does not count sites with no header at all. Dataset, 16 November 2026
Sources
- RFC 6797: HTTP Strict Transport Security (HSTS)
- hstspreload.org: submission requirements and removal
- Cloudflare docs: HTTP Strict Transport Security
- nginx documentation: add_header
- Apache documentation: mod_headers
- AGuard: security dataset of Lithuanian websites, DOI 10.5281/zenodo.24282573
Changes
- Page published; nginx and Apache lines tested on a test server.