
Wiki / Email
Warning: DMARC record
The domain does not tell mail servers what to do with messages that fake your address, so the recipient's mail system has no instruction to stop them. The first record takes 5 minutes and cannot break anything.
What it does not mean. It does not mean your mail is failing to arrive or that someone is already sending in your name. Gmail requires DMARC only from senders of more than 5,000 messages a day (since 1 February 2024); everyone else needs SPF or DKIM.
- In our report
- Warning (yellow), category weight 0.8 of 2.0
- Time to fix
- 5 minutes for the first record; a few weeks of reports before
p=reject - Can it break things
- Not with
p=none. Withquarantineandreject, yes
How to fix it
DMARC is a single TXT record at _dmarc.yourdomain.com. It works only when the domain already has SPF or DKIM. Tighten the policy in three steps, not in one go.
Step 1: watch only
_dmarc TXT "v=DMARC1; p=none; rua=mailto:[email protected]"Nothing changes for your mail. Reports arrive at the rua address and show who sends mail in your domain's name.
Step 2: to spam
_dmarc TXT "v=DMARC1; p=quarantine; rua=mailto:[email protected]"Once the reports show every real sender of yours passing the check: the mail server, the newsletter tool, website forms, invoicing software.
Step 3: reject
_dmarc TXT "v=DMARC1; p=reject; rua=mailto:[email protected]"The final value. In the Cloudflare DNS panel: Type TXT, Name _dmarc, Content is the text inside the quotes.
How to check
dig +short TXT _dmarc.example.comExpected
"v=DMARC1;p=reject;sp=reject;adkim=s;aspf=s"An empty result means there is no record. There must be exactly one: when two v=DMARC1 records are found, both are discarded.
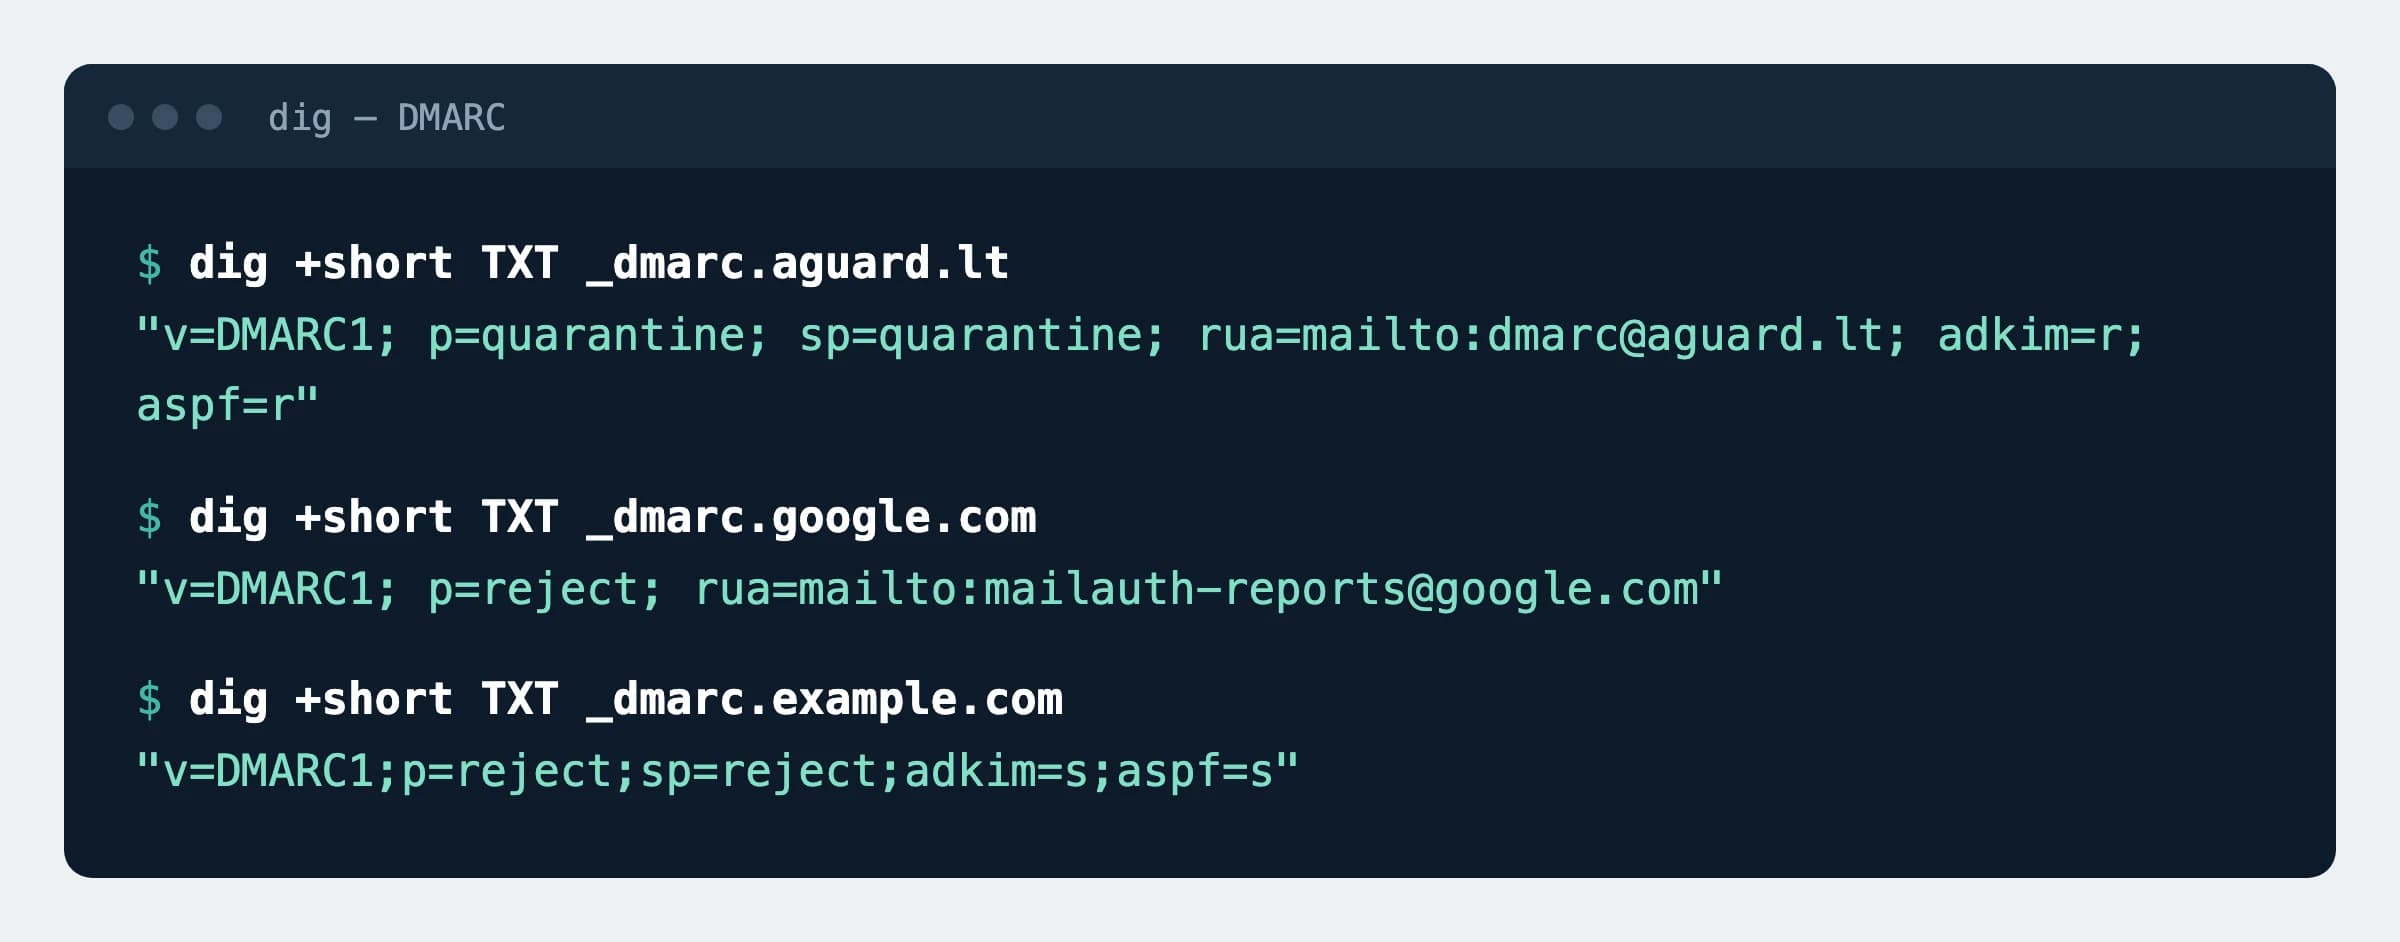
quarantine), google.com and example.com (reject).What can break
- With
p=rejectyour own messages are rejected too when they go through a system that does not sign DKIM with your domain: a newsletter tool, a CRM, online shop notifications. Gmail answers with error550 5.7.26. - When a message is forwarded (from a company address to a personal Gmail, for example) SPF no longer matches. The message passes only if it carries a valid DKIM signature.
- Without
sp, subdomains get the same policy. If a separate system sends fromshop.ormail., find it in the reports before tightening.
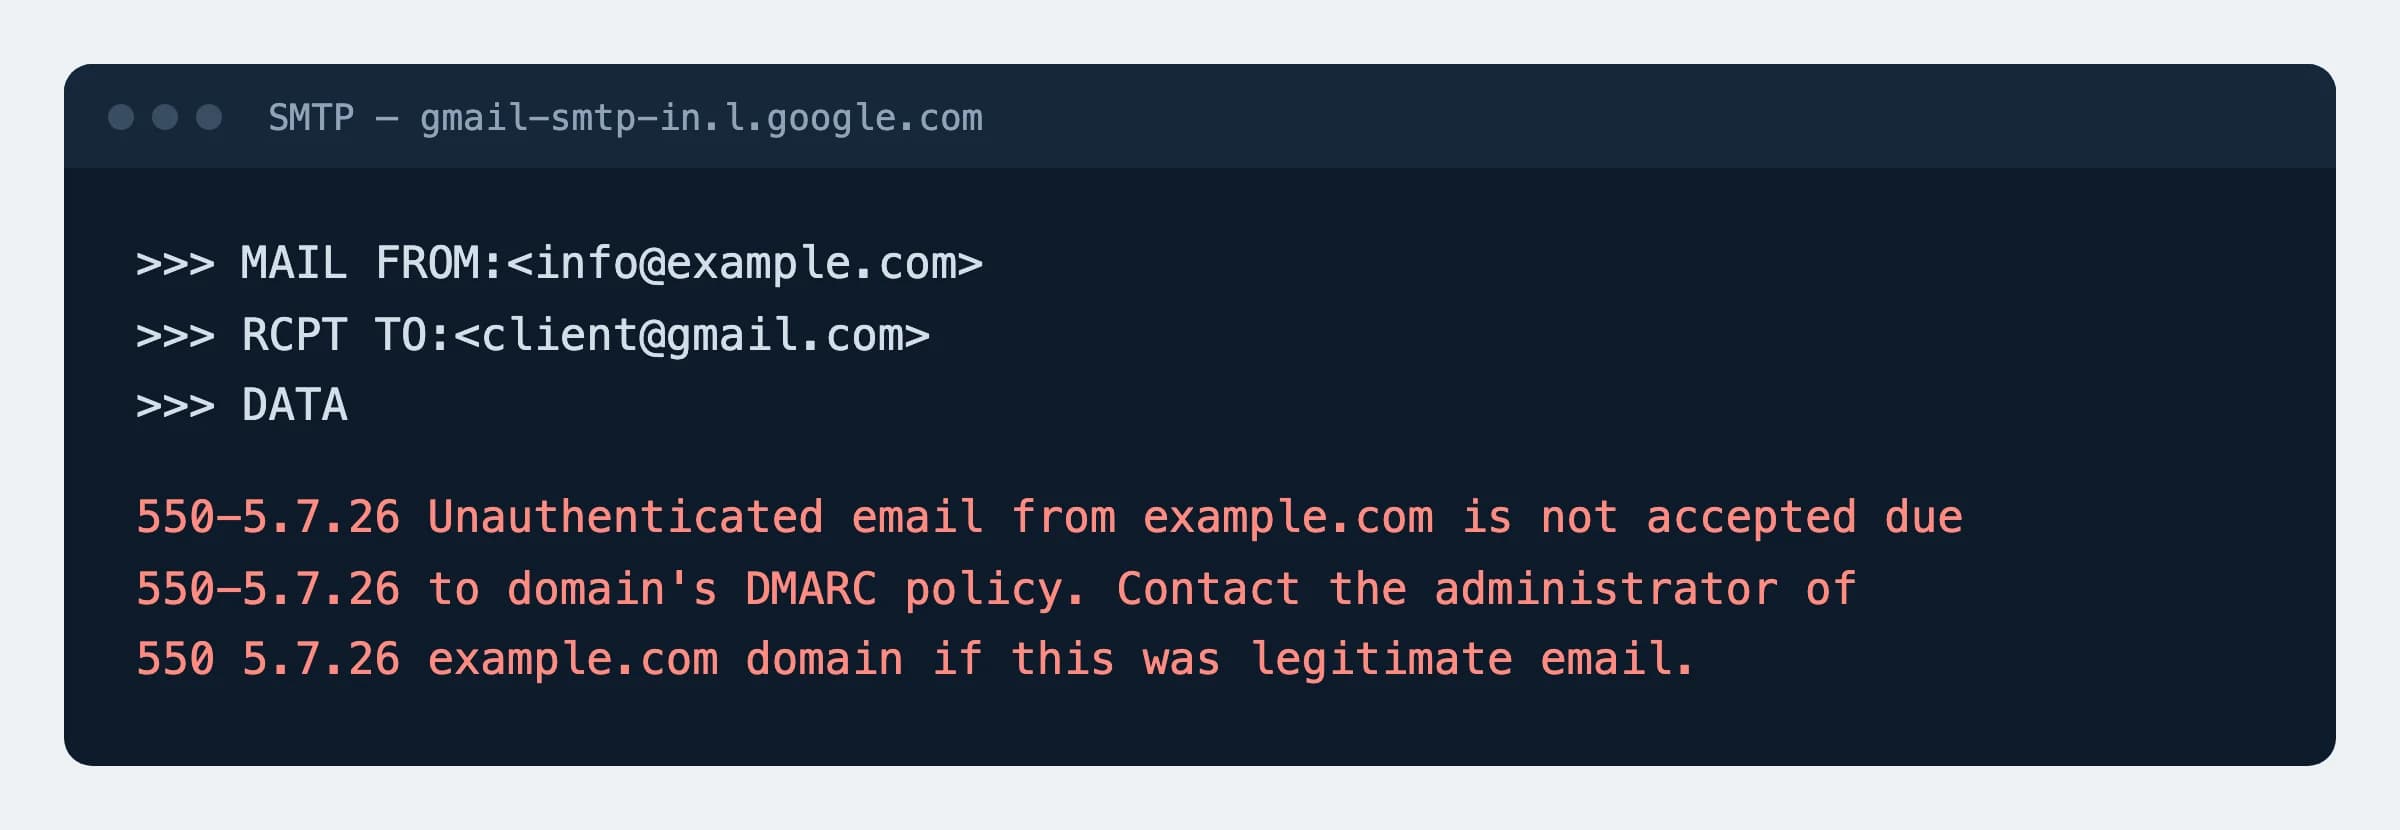
reject and the message fails the check. Text from Google's error reference.Possible values
In May 2026 DMARC became an Internet standard (RFC 9989), replacing RFC 7489 from 2015. Existing records keep working, but several tags changed.
| Tag | What it does | Note |
|---|---|---|
p=none | Take no action, only send reports | For the start; left for good, it does not protect against forgery |
p=quarantine | Treat failing messages as suspicious | They usually land in spam |
p=reject | Reject failing messages | The strongest protection |
sp= | A separate policy for existing subdomains | Without it, p applies to subdomains |
np= | Policy for subdomains that do not exist | New in RFC 9989 |
rua= | Where aggregate reports are sent | Without it you cannot see who sends in your name |
t=y | Test mode | New in RFC 9989; replaces pct |
pct= | Apply the policy to a share of messages | Removed in RFC 9989: do not rely on it in a new record |
Our data
68.5%
of 64,910 inspected .lt domains (44,466) have no DMARC record. Another 25.3% have only p=none, which stops nothing. 6.2% tell receivers to quarantine or reject forged mail. Dataset, 16 November 2026
Sources
- RFC 9989: DMARC (May 2026, obsoletes RFC 7489)
- RFC 7489: DMARC (2015, obsolete)
- Google: email sender guidelines
- Google: Gmail SMTP errors and codes
- AGuard: security dataset of Lithuanian websites, DOI 10.5281/zenodo.24282573
Changes
- Page published; tag table checked against RFC 9989.