
Wiki / Security headers
Warning: X-Frame-Options
Any other website can show your page in an invisible frame and trick a visitor into clicking your button without knowing it. One line and 5 minutes fix it, and it almost never breaks anything.
What it does not mean. It does not mean someone is framing the site already. And if you already send CSP with frame-ancestors, the protection is there: browsers then ignore X-Frame-Options.
- In our report
- Warning (yellow), category weight 1.0 of 2.0
- Time to fix
- 5 minutes
- Can it break things
- Only if another site shows your pages on purpose (a partner frame, a widget)
How to fix it
nginx (tested on 1.26.3)
add_header X-Frame-Options "SAMEORIGIN" always;Apache (tested on 2.4.59, also works in .htaccess)
Header always set X-Frame-Options "SAMEORIGIN"The modern equivalent in CSP
Content-Security-Policy: frame-ancestors 'self'Both headers can be sent together: old browsers read X-Frame-Options, new ones read frame-ancestors.
How to check
curl -sI https://example.com | grep -i x-frame-optionsExpected
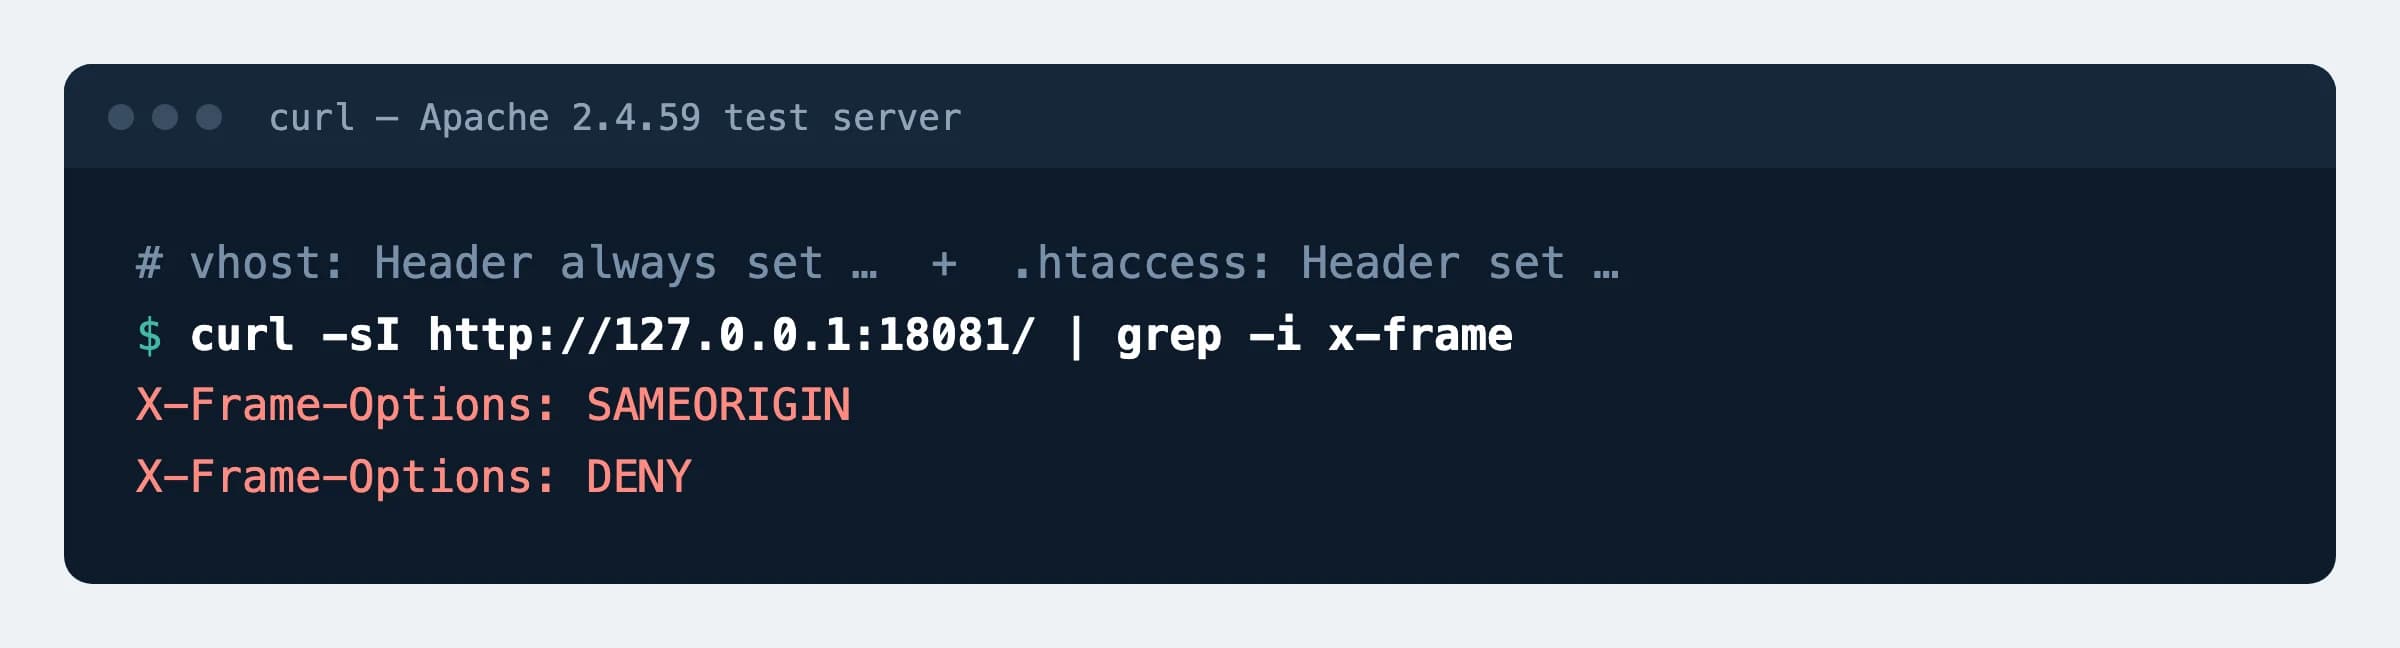
x-frame-options: SAMEORIGINThere must be one line. Two lines mean two sources send the header.
What can break
- If both the server and a plugin or
.htaccessadd the header, the visitor gets two. On the test server Apache withHeader always setin the server config andHeader setin.htaccesssent both:SAMEORIGINandDENY. Keep one source. <meta http-equiv="X-Frame-Options">has no effect: the header works only when the server sends it.- If another site legitimately shows your page (a booking window on a partner's page),
SAMEORIGINmakes it disappear there. Useframe-ancestorswith the partner's address in that case.
Possible values
| Value | What it does | When to choose it |
|---|---|---|
SAMEORIGIN | Only your own site may frame the page | Right for almost everyone |
DENY | Nobody may frame it, not even you | When the site uses no frames at all |
ALLOW-FROM | Obsolete value | Browsers that meet it ignore the whole header. Use frame-ancestors https://partner.example instead |
Sources
- RFC 7034: HTTP Header Field X-Frame-Options
- W3C: Content Security Policy Level 3, frame-ancestors
- MDN (Mozilla): X-Frame-Options header
- nginx documentation: add_header
- Apache documentation: mod_headers
Changes
- Page published; nginx and Apache lines tested on a test server.