
Wiki / Version disclosure
Warning: Server header reveals the version
The web server states its exact version in every response. That is not a hole in itself, but it is the line automated scanners filter on when they look for one specific vulnerable version. Low urgency: one line fixes it.
What it does not mean. It does not mean the server is outdated or vulnerable. The reverse holds too: hiding the number patches nothing. An old server stays exactly as exploitable and only drops out of the simplest filter. On Debian and similar systems the number can also look older than the software is, because security fixes are backported into the same version without changing it.
- In our report
- Warning (yellow), category weight 0.5 of 2.0
- Time to fix
- 5 minutes plus a reload of the server configuration
- Can it break things
- Only if you put
ServerTokensinto .htaccess: the site returns 500
How to fix it
Hiding the version takes a minute, but the real job is updating the server. Do both, the update first.
nginx (tested on 1.26.3)
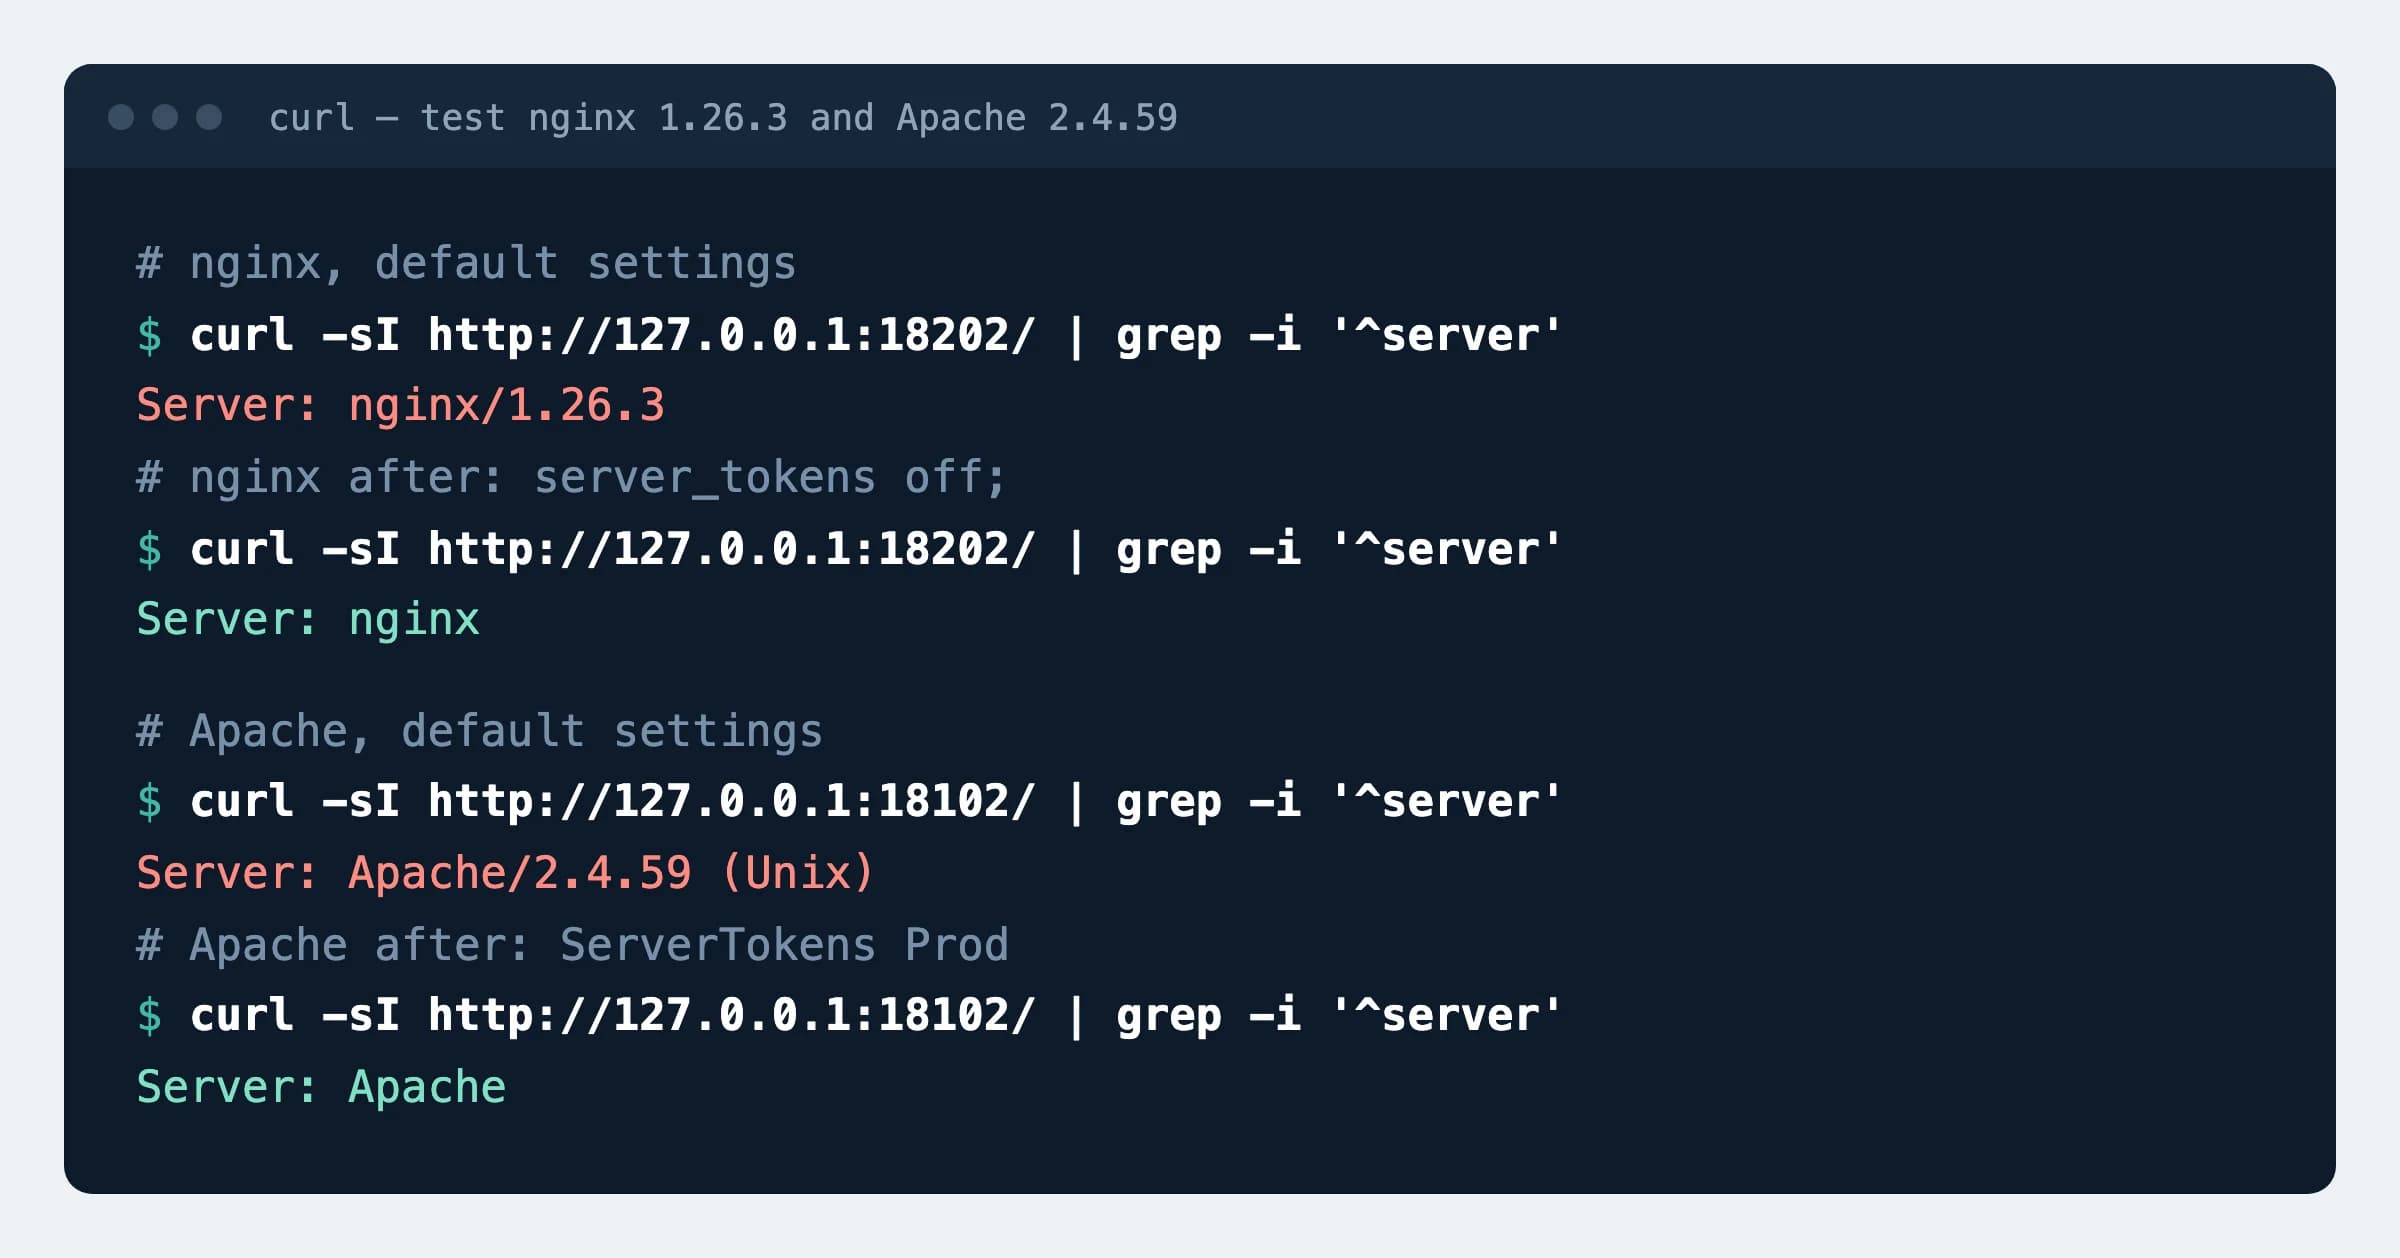
server_tokens off;Goes into http, server or location. Before: Server: nginx/1.26.3, and the same string at the bottom of error pages. After: Server: nginx in both places. The word nginx stays: only the commercial nginx can switch the header off entirely, and stock 1.26.3 rejects the third-party more_clear_headers as an unknown directive.
Apache (tested on 2.4.59)
ServerTokens Prod
ServerSignature OffMain server configuration only: ServerTokens applies to the whole server and cannot be set per virtual host. Before: Server: Apache/2.4.59 (Unix). After: Server: Apache. ServerSignature Off is the default; if someone switched it On, the version is printed again at the bottom of error pages. On shared hosting only the provider can change this setting.
How to check
curl -sI https://example.com | grep -i '^server'Expected
server: nginxNo digits should remain in the value. If the site sits behind Cloudflare or another proxy you will see the proxy's name (aguard.lt answers server: cloudflare), not your own server's.
What can break
ServerTokensin .htaccess: our test Apache 2.4.59 answered every request with 500 and logged “ServerTokens not allowed here”.ServerSignatureis allowed in .htaccess.- The Apache documentation advises against going below
Min, because it makes interoperability problems harder to debug, and says outright that hiding the header does nothing to make the server more secure. If your monitoring or inventory tool reads the version from the header, it will stop seeing it.
Possible values
Apache ServerTokens values and what our test 2.4.59 returned with each. The report line stays yellow as long as the header contains a single digit.
| Value | What the server sends | Report line |
|---|---|---|
Full (default) or OS | Server: Apache/2.4.59 (Unix) | Warning |
Min | Server: Apache/2.4.59 | Warning |
Minor | Server: Apache/2.4 | Warning |
Major | Server: Apache/2 | Warning |
Prod | Server: Apache | OK |
Our data
0.25%
of 73,386 inspected .lt websites (183) ran Apache 2.2 or older. The final release of the 2.2 branch, 2.2.34, came out in July 2017; it gets no security fixes any more. Dataset, 16 November 2026
Sources
- nginx documentation: server_tokens
- Apache documentation: ServerTokens
- Apache documentation: ServerSignature
- Apache HTTP Server Project: end of life of the 2.2 branch
- Debian security FAQ: why fixes are backported to the old version
- AGuard: security dataset of Lithuanian websites, DOI 10.5281/zenodo.24282573
Changes
- Page published; nginx and Apache lines tested on test servers.