
Wiki / Reputation
Risk: Domain blocklist check
Spamhaus counts your domain among those used for spam, phishing or malware. Mail filters that use the DBL look for listed domains inside the messages themselves, so any message that contains a link to your site or your address can be rejected or filed as spam, whoever sent it. Deal with it today.
What it does not mean. It does not prove the site is hacked at this moment: Spamhaus does not scan websites, it reacts to abuse it sees in mail and traffic. Nor is it a verdict on your IP address: the DBL lists names only. Codes 127.0.1.102–106 mean that a specific hostname of a compromised site is listed, not the whole domain.
- In our report
- Risk (red), the highest category weight, 2.0
- Time to fix
- An approved removal applies at once, in some systems within 24 hours. Finding and removing the cause takes longer
- Can it break things
- Ask for removal before the clean-up and the domain is listed again once the activity is detected
How to fix it
The order matters: the cause first, the request second. Entries also expire by themselves when the listing criteria are no longer met, but only then.
1. What is listed (tested with dig 9.10.6)
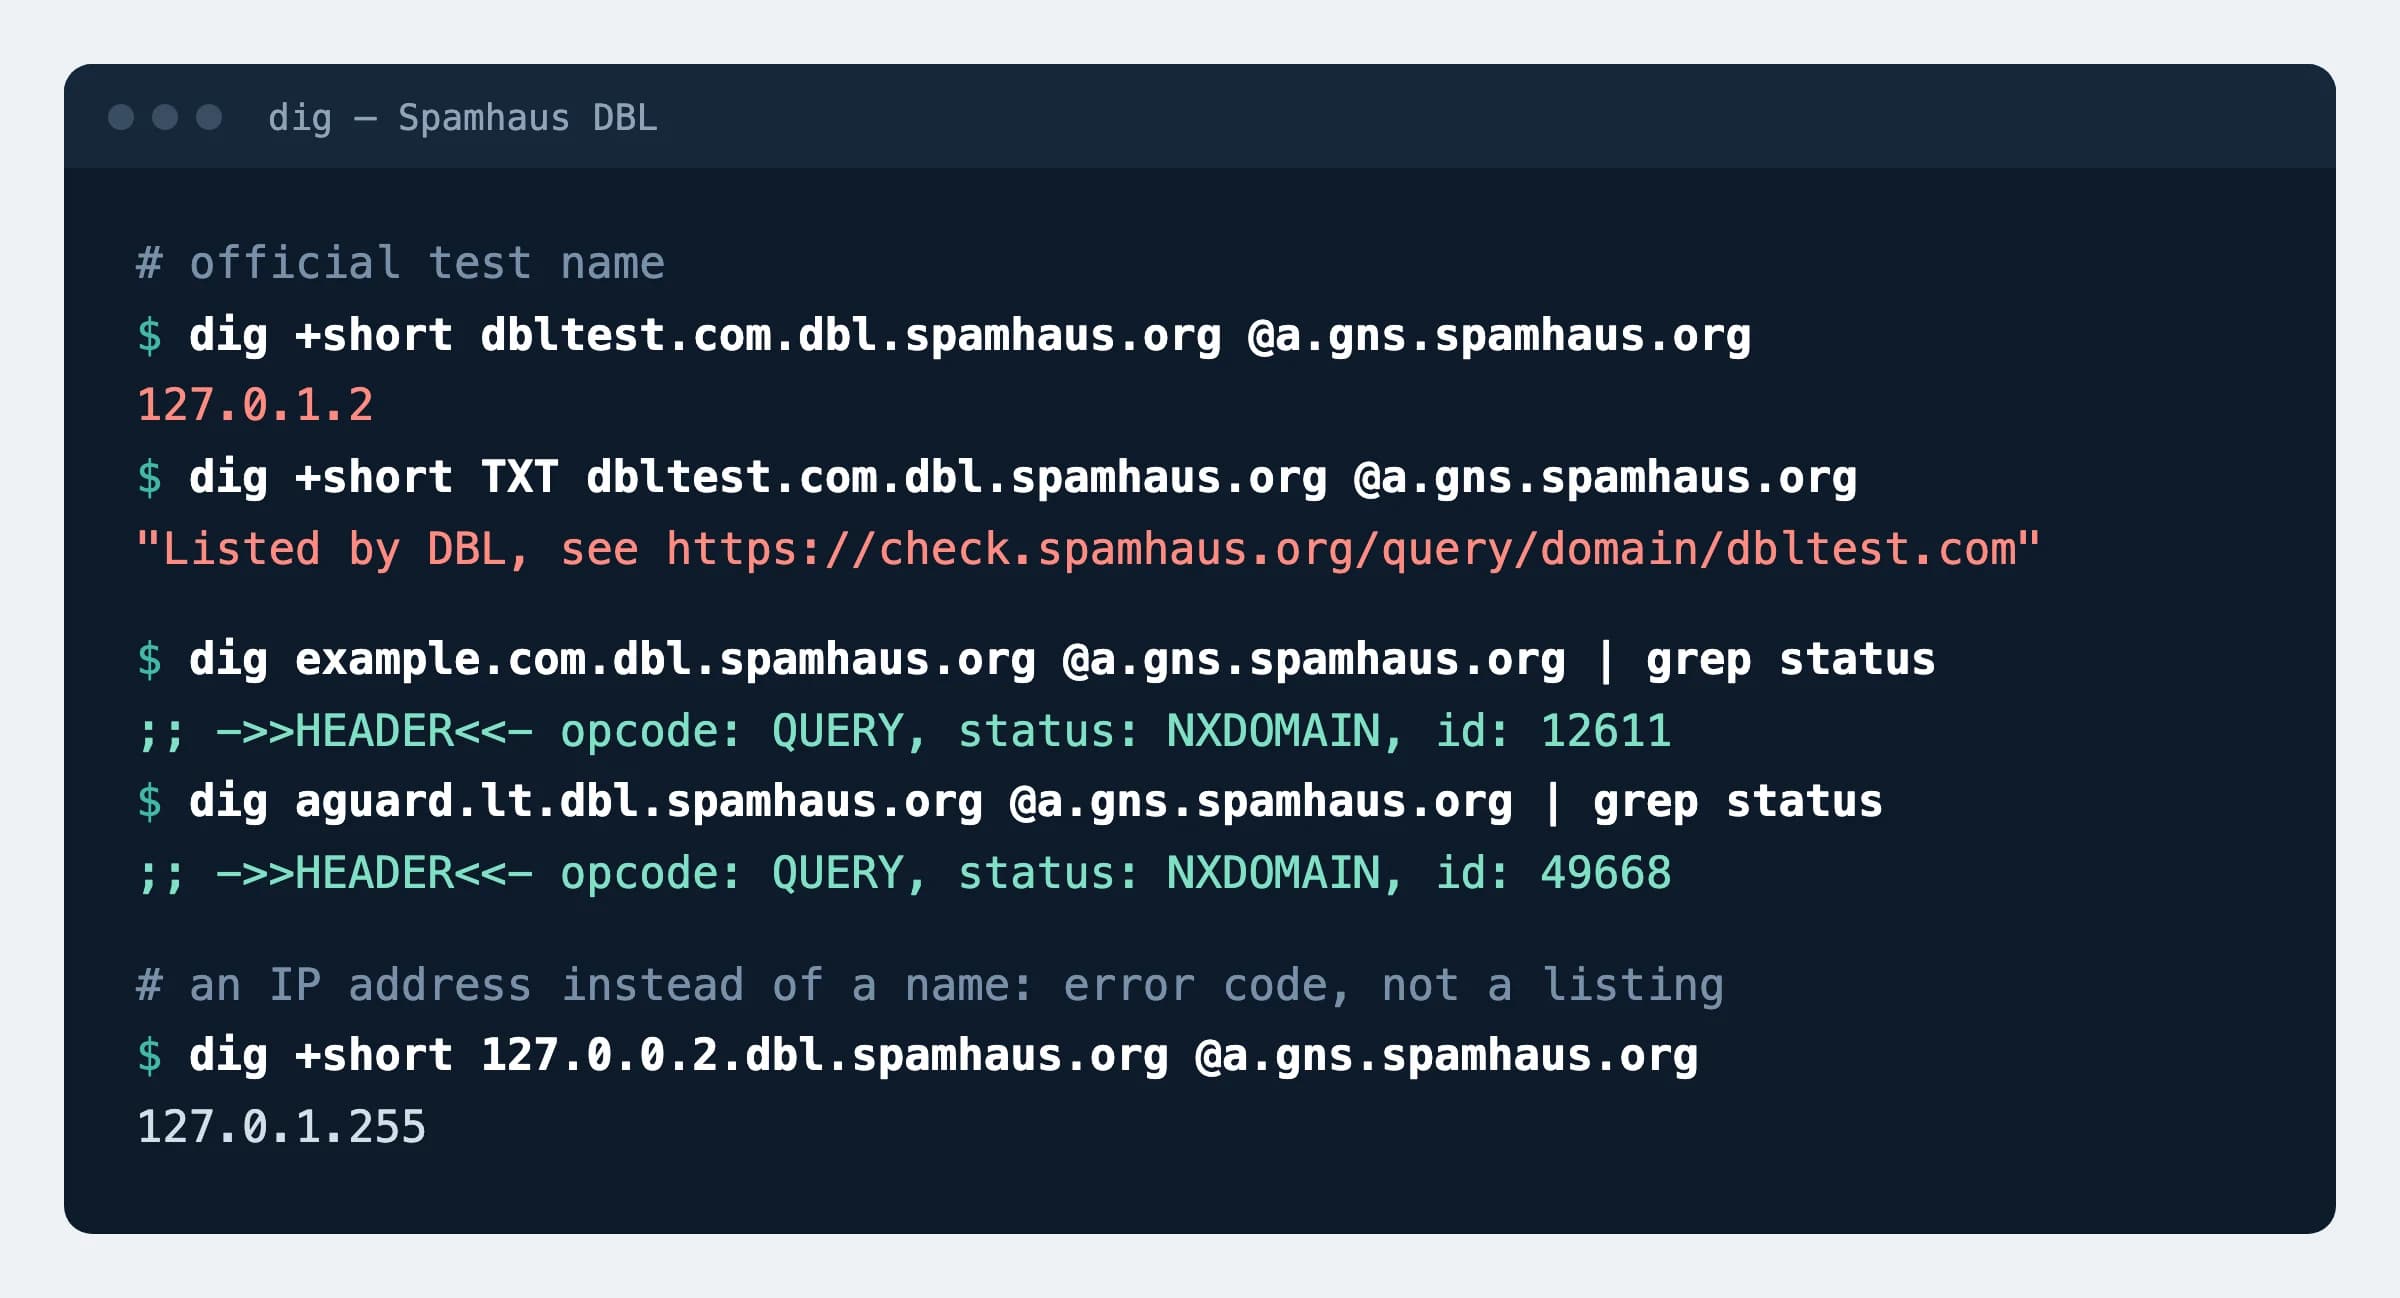
dig +short dbltest.com.dbl.spamhaus.org
dig +short TXT dbltest.com.dbl.spamhaus.orgPut your domain in place of the official test name dbltest.com. The first command returns the code (see the table), the second the address of the entry at check.spamhaus.org.
2. Hacked site: recently changed PHP files (tested with GNU find 4.9.0 and macOS find)
find /var/www/example.com -name '*.php' -mtime -30A starting point, not proof: an intruder can fake a file date. Look at PHP files in upload folders first. The order Spamhaus gives for a compromised site: take it offline if possible, remove the infected files, update the CMS and plugins, secure the server, change all passwords.
3. Removal request
https://check.spamhaus.orgThe only place where DBL entries are removed. It is free; Spamhaus calls any offer of paid removal a scam. Using the form does not guarantee removal.
How to check
In the second query, replace example.com with your domain.
dig +short dbltest.com.dbl.spamhaus.org; dig +short example.com.dbl.spamhaus.orgExpected
127.0.1.2The single line belongs to the test name and shows that your resolver gets answers; nothing should follow it for your domain. According to Spamhaus, example.com will never be listed. If the test name returns nothing either, you are asking through a public resolver: we queried a Spamhaus name server directly (@a.gns.spamhaus.org).
What can break
- It is not only mail from your domain that suffers. Spamhaus tells receivers to check the sender address domain, the server's HELO name, reverse DNS and the domains found in message headers and body. A receiver using the DBL can therefore hold a message sent from a different mail system if it links to your site.
- For a legitimate domain, code
127.0.1.2usually has to do with mail and hosting. Spamhaus lists: bulk mail without confirmed opt-in, a mail server without proper reverse DNS and HELO name, hosting on a network that tolerates spam. The reputation of an unknown domain starts as poor. - A check through public resolvers misleads: on 18 November 2026 the test name returned
127.255.255.254through 1.1.1.1 and “not listed” through 8.8.8.8.
Possible values
Codes from the Spamhaus DBL documentation (checked on 18 November 2026). “Abused legit” is a legitimate site that was compromised, usually through its CMS or stolen hosting credentials.
| Code | What it means |
|---|---|
127.0.1.2 | Spam domain |
127.0.1.4 | Phishing domain |
127.0.1.5 | Malware domain |
127.0.1.6 | Botnet command-and-control (C&C) domain |
127.0.1.102 | Abused legit: spam |
127.0.1.103 | Abused spammed redirector or link shortener |
127.0.1.104 | Abused legit: phishing |
127.0.1.105 | Abused legit: malware |
127.0.1.106 | Abused legit: botnet C&C |
127.0.1.255 | Error: an IP address was queried. The DBL always answers “listed” to such a query |
127.255.255.254 | Error: query through a public resolver. Not a listing |
Sources
- Spamhaus: DBL FAQ (codes, test names, compromised sites, removal)
- Spamhaus: Domain Blocklist (where the domain is checked)
- Spamhaus: DNSBL usage FAQ (error codes, public resolvers)
- Spamhaus: IP and Domain Reputation Checker
Changes
- Page published; code table checked against the Spamhaus DBL documentation, dig queries run the same day.